Le blog Workstation
Security
Articles étiquetés Security.
Placez vos applications internes derrière votre VPN, sans les reconstruire
Les sites de préproduction et les panneaux d'administration sont souvent « privés » grâce à une liste d'adresses IP autorisées. Placez-les derrière le VPN Zero Trust wslvpn, appliqué en périphérie par WSLProxy : vérifiez le tunnel et la personne, refusez en cas d'échec et voyez pourquoi quelqu'un a été bloqué. Un champ par domaine, aucune modification des applications, aucun rechargement.
 Balinder WaliaLire
Gateway API Shifts Cluster Networking: An Ownership Model for the Edge
Ingress is frozen and Ingress NGINX is retired. Gateway API replaces one shared object with resources owned by platform and application teams, joined by explicit handshakes. Here is what that means for platform design, RBAC, topology and CRD ownership.
Agentic AI in Production: Permissions, Approval Gates, Traces and Evals
A practical playbook for running AI agents in production: classify every tool by side effect, gate mutations behind a human, set hard stop conditions, trace each step with OpenTelemetry and evaluate continuously.
MCP for DevOps: Give Agents Pipeline Context Without the Keys
How platform teams can use the Model Context Protocol safely: start with read-only servers and scoped identities behind a gateway, trace every tool call, and add write tools only behind human approval. Includes RBAC, tool and task examples.
Gemini 4 Argon : ce que cela signifie pour votre équipe, et où l'utiliser en premier
Gemini 4 Argon est conçu pour travailler pendant des heures sur un seul problème mesurable. Voici ce qui est sorti, les coûts réels et comment le piloter en toute sécurité sur votre propre backlog.
Balinder WaliaLire 
WSL Vault pour la conformité : un locataire n'ouvre jamais les secrets d'un autre
Comment WSL Vault isole cryptographiquement les locataires que sont les applications, les équipes et les environnements, afin qu'un jeton de type racine volé ne puisse pas vider l'ensemble du parc, et pourquoi le double contrôle par locataire l'emporte sur la prolifération des secrets.
Balinder WaliaLire 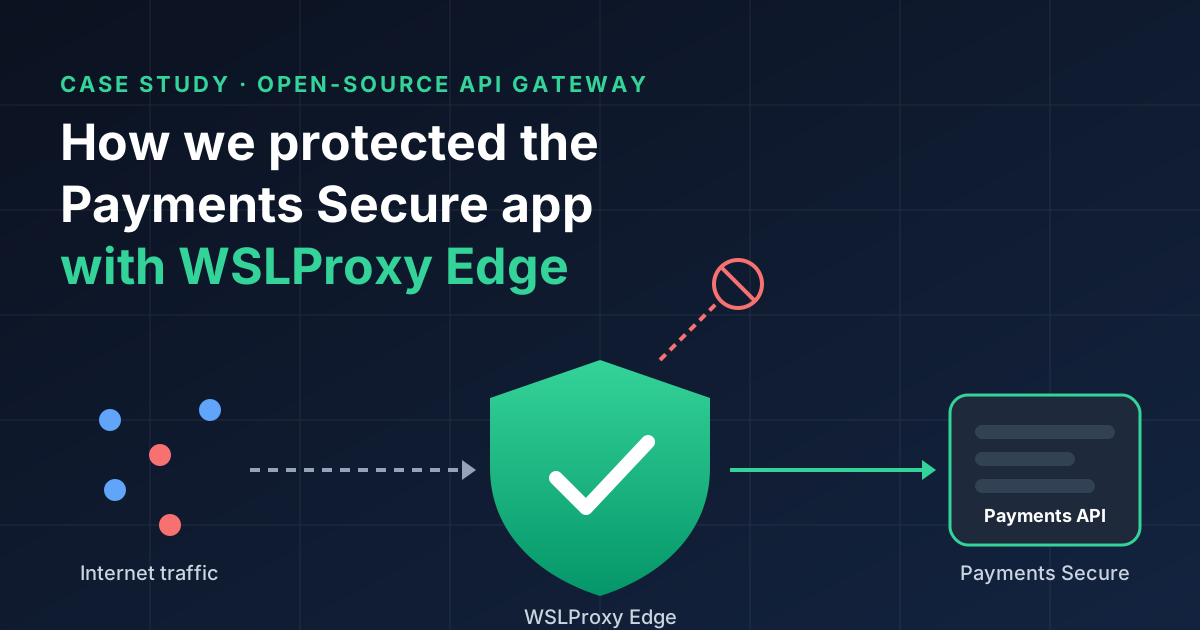
How We Protected the Payments Secure FinTech App with WSLProxy Edge, an Open-Source API Gateway
How we put WSLProxy Edge, our open-source API gateway, in front of Payments Secure (payments-secure.fictionally.org): real-IP checks, scanner detection, login throttling and audit logs, rolled out safely in audit mode.
Balinder WaliaLire 
WSLVault: Why AI Agents Need Cryptographic Secrets Isolation
AI agents use secrets at machine speed across tools and tenants. WSLVault seals per tenant so a shared platform never leaks another team's plaintext.
Balinder WaliaLire