Der Workstation-Blog
Security
Beiträge mit dem Tag Security.
Interne Anwendungen hinter Ihr VPN stellen, ohne sie neu zu bauen
Staging-Sites und Admin-Panels sind oft nur dank einer IP-Allowlist „privat“. Stellen Sie sie hinter das Zero-Trust-VPN wslvpn, durchgesetzt am WSLProxy-Edge: Tunnel und Person prüfen, im Fehlerfall sperren und sehen, warum jemand blockiert wurde. Ein Feld pro Domain, keine Änderungen an der Anwendung, kein Neuladen.
 Balinder WaliaLesen
Gateway API Shifts Cluster Networking: An Ownership Model for the Edge
Ingress is frozen and Ingress NGINX is retired. Gateway API replaces one shared object with resources owned by platform and application teams, joined by explicit handshakes. Here is what that means for platform design, RBAC, topology and CRD ownership.
Agentic AI in Production: Permissions, Approval Gates, Traces and Evals
A practical playbook for running AI agents in production: classify every tool by side effect, gate mutations behind a human, set hard stop conditions, trace each step with OpenTelemetry and evaluate continuously.
MCP for DevOps: Give Agents Pipeline Context Without the Keys
How platform teams can use the Model Context Protocol safely: start with read-only servers and scoped identities behind a gateway, trace every tool call, and add write tools only behind human approval. Includes RBAC, tool and task examples.
Gemini 4 Argon: Was es für Ihr Team bedeutet und wo Sie es zuerst einsetzen sollten
Gemini 4 Argon ist dafür gebaut, stundenlang an einem messbaren Problem zu arbeiten. Hier erfahren Sie, was veröffentlicht wurde, was es wirklich kostet und wie Sie es sicher an Ihrem eigenen Backlog erproben.
Balinder WaliaLesen 
WSL Vault für Compliance: Kein Mandant öffnet jemals die Secrets eines anderen
Wie WSL Vault App-, Team- und Umgebungsmandanten kryptografisch voneinander isoliert – sodass ein gestohlenes Token im Root-Stil nicht die gesamte Landschaft leeren kann – und warum Zwei-Mandanten-Kontrolle besser ist als Secrets-Wildwuchs.
Balinder WaliaLesen 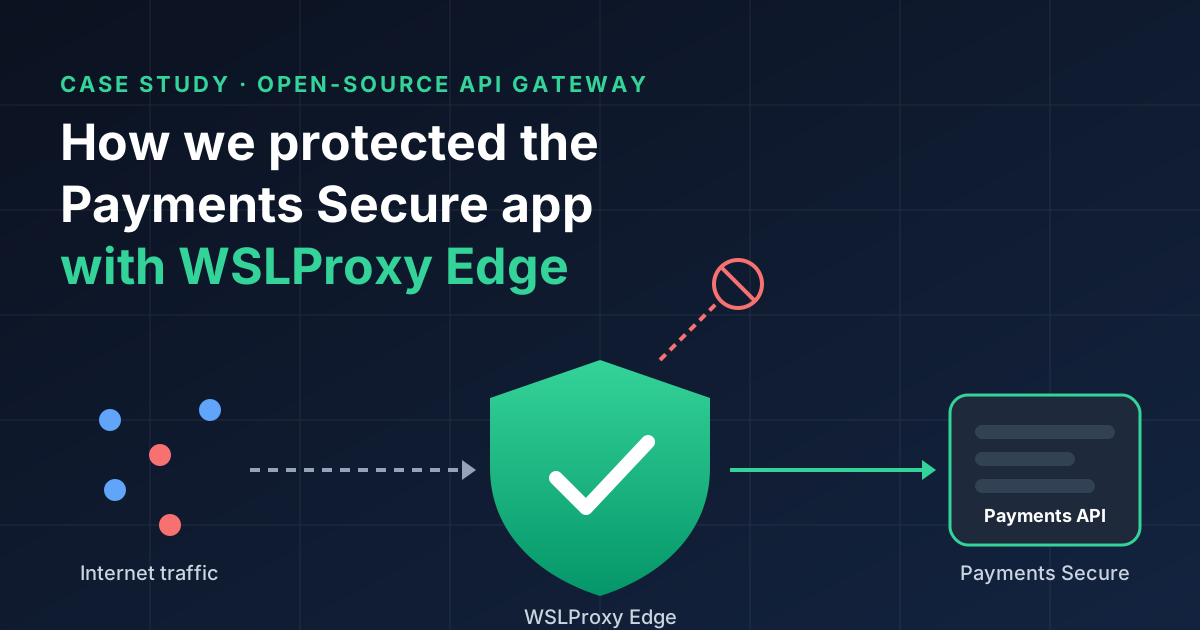
How We Protected the Payments Secure FinTech App with WSLProxy Edge, an Open-Source API Gateway
How we put WSLProxy Edge, our open-source API gateway, in front of Payments Secure (payments-secure.fictionally.org): real-IP checks, scanner detection, login throttling and audit logs, rolled out safely in audit mode.
Balinder WaliaLesen 
WSLVault: Why AI Agents Need Cryptographic Secrets Isolation
AI agents use secrets at machine speed across tools and tenants. WSLVault seals per tenant so a shared platform never leaks another team's plaintext.
Balinder WaliaLesen