kube-proxy-free datapath shifts cluster ops to new solutions

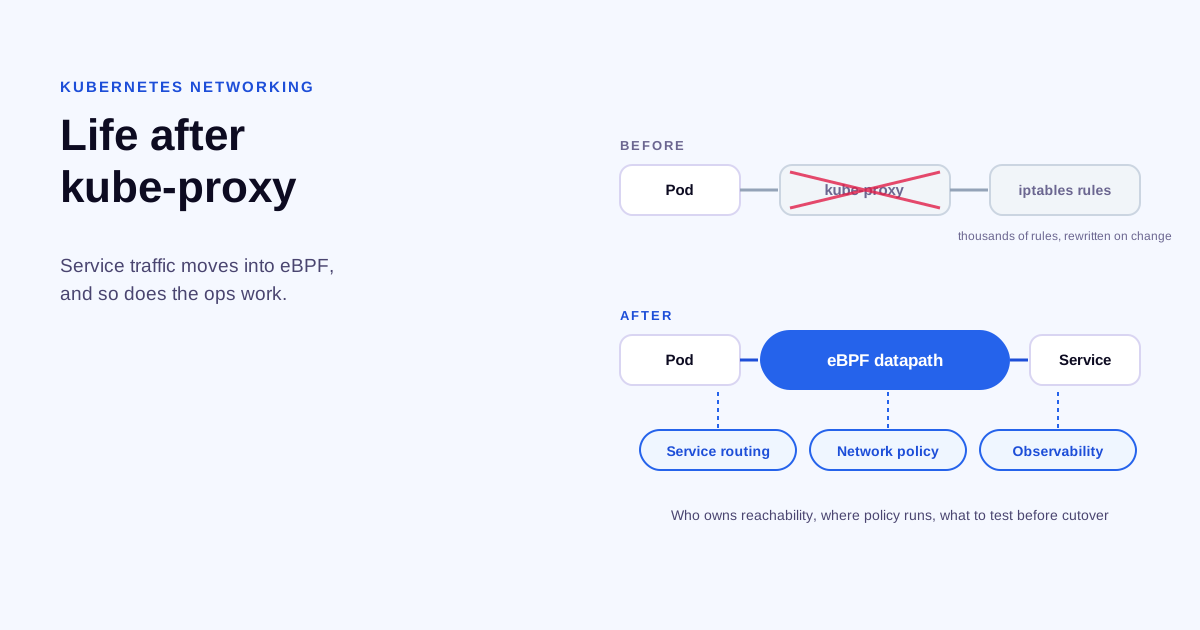
Removing kube-proxy from the data path changes who owns service reachability, where policy is enforced, and what the cluster team must validate before a release touches customer data. The shift moves traffic handling out of a per-node daemon and into higher-level ingress and API gateway layers.
kube-proxy removal and its effects on cluster operators
For teams running regulated workloads, kube-proxy has been the default that made ClusterIP services reachable inside the cluster. Operators relied on it for consistent service discovery without building explicit ingress per service. The recent Kubernetes discussion around IPVS signals why that default is under pressure.
The ipvs backend was originally designed to fix two different kinds of performance problems in the iptables backend [1]. The ipvs backend solved both of these scaling problems [1]. The ipvs backend will no longer be available to Kubernetes users on RHEL due to Red Hat's plan to remove the iptables API entirely from Red Hat Enterprise Linux [1].
In environments that standardize on RHEL for support and compliance, that removal forces a decision early in the platform lifecycle. Cluster operators can no longer assume an IPVS fallback will be available on the host OS. The effect is operational: service reachability must be provided by alternatives that are explicitly deployed, versioned and audited.
That means the team owning the control plane also owns the data-path contract.
Alternative solutions for ingress controllers and API gateways
With kube-proxy out of the picture, the common patterns are OpenAPI-driven gateways, the standard Gateway API, and purpose-built load balancers used as API gateways.
Gateway API is designed to provide a more flexible, extensible, and powerful way to manage traffic to your services [2]. Gateway API is just weeks away from a GA release. It provides a standard Kubernetes API for ingress traffic control [2]. Gateway API commits to supporting the 5 latest Kubernetes minor versions. That means that Gateway API currently supports Kubernetes 1.24+ [2].
Kusk Gateway is an open-source Ingress controller / API Gateway that makes your OpenAPI definition the source-of-truth for both functional and operational aspects of your APIs [3]. API mocking has been implemented in Kusk Gateway [3]. Kusk Gateway now generates its own webhook certificates internally, removing the need for CertManager [3]. Kusk Gateway includes a command-line utility for creating Kusk Gateway API resources from your OpenAPI specification document [3].
An API gateway handles load balancing, security, rate limiting, monitoring, and other cross-cutting concerns for API services [4]. HAProxy can route based on any information found in the HTTP request, including portions of the URL path, query string, and HTTP headers [4]. Due to its speed, high availability and reliability, HAProxy can be used as a API gateway [4]. The API gateway becomes the orchestration layer that forwards requests so that frontend code and backend API endpoints are not tightly coupled [4].
Comparison of options
| Option | Control model | Compliance artifacts | Operational overhead |
|---|---|---|---|
| Kusk Gateway | OpenAPI-driven, design-first | OpenAPI spec is source of truth | Lower cert management; internal webhook certs |
| Gateway API | Standard Kubernetes API for ingress | Declarative Gateway/HTTPRoute objects | Requires controller adoption, version support |
| HAProxy as API gateway | Config-driven load balancer | Explicit config, header/path routing | Manual or templated config, high availability tuning |
Benefits and challenges of adopting new solutions
API-first gateways make the surface area explicit. OpenAPI definitions can be reviewed, versioned and signed before promotion. Mocking at the OpenAPI level lets QA teams test integrations without touching production data stores [3].
Gateway API standardizes the API for ingress traffic control, which reduces vendor lock-in and simplifies multi-cloud posture reviews. HAProxy’s ability to route based on any information found in the HTTP request gives fine-grained control for feature flags and tenant isolation [4].
Challenges are equally real. Wildcard routes can make the routing table hard to reason about in a distributed environment [5].
Migrations also create interface compatibility risk. API gateways can simplify migrating to new services by maintaining compatibility with existing interfaces [5].
Cost visibility shifts too. On managed platforms, cluster management fees accumulate regardless of size. A flat cluster management fee of $0.10 per cluster per hour applies to all GKE clusters [6]. The GKE free tier provides $74.40 in monthly credits per billing account [6]. Unused free tier credits are not rolled over [6].
Real-world examples and implications for cluster operators
Consider a platform that processes filings in a narrow window. Operators need predictable ingress latency and the ability to roll back a gateway rule without restarting the control plane. With kube-proxy removed, service IP routing is no longer implicit. The team must validate that Gateway API routes, Kusk Gateway resources, or HAProxy backends are reconciled before the window opens.
In HealthTech, PHI access requires logging every request path. An API gateway handles load balancing, security, rate limiting, monitoring, and other cross-cutting concerns for API services [4].
For environments standardizing on RHEL, the removal of iptables-based backends on RHEL [1] means the platform team must document which OS versions are supported and how service reachability is provided.
A simple request flow after kube-proxy removal looks like this:
Future directions and next steps for cluster operators
Operators should treat the data path as a product, not a default. Start by inventorying all services that relied on ClusterIP reachability and map them to an explicit gateway contract.
Pilot Gateway API on non-critical namespaces first. Because Gateway API currently supports Kubernetes 1.24+ [2], verify the control plane version and controller compatibility before committing.
If OpenAPI governance is already in place, evaluate Kusk Gateway for its design-first workflow and internal webhook certificate generation [3]. Automate resource generation from OpenAPI as part of CI/CD using the included CLI utility [3].
For performance-critical edges, keep HAProxy as a proven API gateway option due to its speed, high availability and reliability [4]. Use explicit routing rules rather than wildcards to keep the routing table auditable [5].
The kube-proxy-free future does not eliminate service networking. It makes the choice explicit and moves the responsibility to teams who can own security, auditability and cost.
References
- Scheduling the removal of the kube-proxy IPVS backend — kubernetes.io
- Introducing ingress2gateway; Simplifying Upgrades to Gateway API | Kubernetes — kubernetes.io (29 October 2023)
- Kusk-gateway OpenAPI-driven Kubernetes Ingress Controller Beta — kubeshop.io (31 March 2022)
- Using HAProxy as an API gateway, part 1 [introduction] — haproxy.com (1 October 2018)
- Building DigitalOcean's API gateway - Maurício Linhares' ramblings — mauricio.github.io (16 January 2021)
- Google Kubernetes Engine pricing — cloud.google.com (4 March 2020)