Cloudflare WAF Blocks Java4Shell Attacks

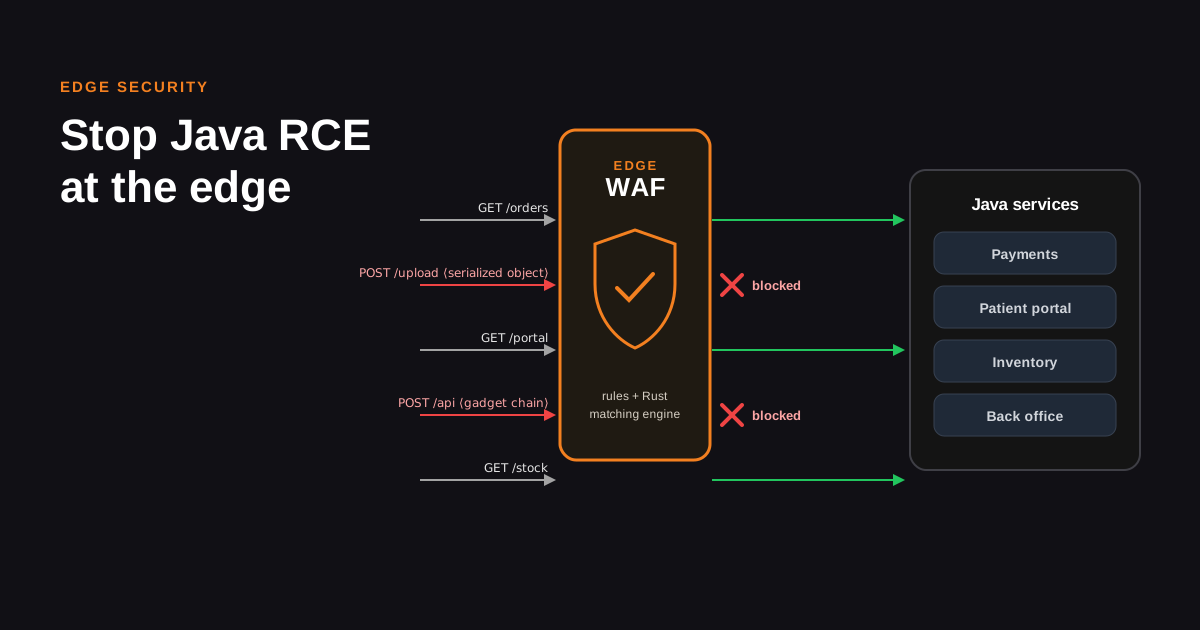
Java4Shell is a class of remote code execution attacks against Java-based services. For teams in manufacturing, supermarkets, banking, education, HealthTech, FinTech and tax returns, the exposure is operational: these sectors run long-lived Java applications for back-office processing, payment handling, patient or student portals, and inventory systems. A successful exploit can mean downtime on a production line, disruption to point-of-sale or payment flows, or exposure of regulated personal data. Because the risk profile is similar across these industries — internet-exposed Java services handling untrusted input — the protection strategy is the same everywhere: inspect traffic at the edge before it reaches the application.
What is Java4Shell and Why is it a Threat?
Java4Shell refers to exploitation chains that leverage Java deserialization and class-loading behavior to achieve remote code execution. Attackers deliver payloads that trigger heap corruption and subsequent code execution.
For developers in regulated sectors, the consequence is operational and compliance risk. Public-facing endpoints that accept serialized data, file uploads, or query parameters can reach a vulnerable Java runtime, and a single crafted request can lead to full compromise.
The Cloudflare WAF blocks more than 57 billion cyber threats per day [1], which illustrates the scale of automated probing that these services face.
How Cloudflare WAF Protects Against Java4Shell
Cloudflare WAF provides edge-level inspection with a new matching engine written in Rust and supporting the wirefilter syntax [1]. The new WAF ships with updated rulesets that provide better control separating rule status from action [1], and allows for global configuration, deploying the same configuration across the entire account [1].
Protection for paid plans has been released as part of the Cloudflare Managed Ruleset with Ruleset ID efb7b8c949ac4650a09736fc376e9aee [2]. The rule is enabled by default with the Log action, because blocking by default could cause false positives on legitimate Base64 traffic [2].
While the managed rule is the primary way to block malformed Base64 triggers at the edge, Cloudflare WAF Attack Score can offer an additional, complementary layer of protection against Java4Shell [2]. Specifically, on Enterprise plans the remote code execution sub-score cf.waf.score.rce is available [2].
If an exploit chain pairs the initial heap-corruption trigger with a second-stage payload such as shell execution primitives or Java class-loading gadgets tucked into another header, query parameter, or request body, cf.waf.score.rce can detect and score that secondary payload as malicious [2].
Implementing Java4Shell Protection with Cloudflare WAF
Implementation is done in the Cloudflare dashboard and can be codified via the API. The steps assume you already proxy the domain through Cloudflare.
- Verify plan eligibility. Protection for paid plans has been released as part of the Cloudflare Managed Ruleset [2].
- Enable the managed ruleset on the zone. In Dashboard > Security > WAF > Managed Rules, ensure the Cloudflare Managed Ruleset is active. The Java4Shell rule set is part of Ruleset ID efb7b8c949ac4650a09736fc376e9aee [2].
- Review default action. The rule ships with Log action by default to avoid false positives on legitimate Base64 traffic [2]. For high-risk public endpoints, consider a test period in Log mode before moving to Block or Challenge.
- Optional: layer Attack Score. For Enterprise customers, create a Firewall Rule that raises the WAF score threshold using cf.waf.score.rce. This adds coverage for secondary payloads such as shell execution primitives or Java class-loading gadgets [2].
- Monitor logs. Enable Logpush or review WAF Events to confirm the rule is firing on expected patterns without impacting legitimate traffic.
- Adjust configuration as needed. Tune action per rule or per path, and document exceptions for internal tools that legitimately use Base64.
Example API check for the ruleset status:
curl -X GET "https://api.cloudflare.com/client/v4/accounts/{ACCOUNT_ID}/rulesets/{efb7b8c949ac4650a09736fc376e9aee}" \
  -H "Authorization: Bearer {API_TOKEN}" \
  -H "Content-Type: application/json"
Action selection trade-off:
| Action | When to use | Risk |
|---|---|---|
| Log | Initial rollout, low confidence | No blocking, visibility only |
| Block | Confirmed attack traffic, no business impact | Potential false positive impact |
| Challenge / JS Challenge | Mixed traffic with legitimate Base64 | Balances security and usability |
Best Practices for Securing Your Application
WAF is one layer. For manufacturing, supermarkets, banking, education, HealthTech, FinTech and tax returns, uptime is critical, data is sensitive, and change windows are narrow.
- Keep the Managed Ruleset enabled and up to date. Cloudflare ships updated rulesets that provide better control separating rule status from action [1].
- Use global configuration to deploy the same configuration across your entire account [1], ensuring consistent protection for dev, staging and production zones.
- Limit deserialization surfaces. Review Java services for unnecessary endpoints that accept serialized objects, and enforce strict input validation at the application layer.
- Monitor WAF Attack Score trends. Cloudflare WAF Attack Score can offer an additional, complementary layer of protection against Java4Shell [2].
- Test changes in Log mode first. The rule is enabled by default with the Log action, because blocking by default could cause false positives on legitimate Base64 traffic [2].
- Combine WAF with an Application Firewall and Intrusion Detection System, and forward events to a Security Information and Event Management system for correlation.
Conclusion: Safeguarding Your Application with Cloudflare WAF
Java4Shell attacks target unsafe handling of serialized or Base64-encoded input that can lead to remote code execution. For developers supporting manufacturing, retail, banking, education, HealthTech, FinTech and tax systems, the impact of a breach is operational downtime and regulatory exposure.
Cloudflare WAF provides a managed, edge-level control point. The WAF blocks more than 57 billion cyber threats per day [1] using a new matching engine written in Rust and supporting the wirefilter syntax [1]. Protection for paid plans is available as part of the Cloudflare Managed Ruleset with Ruleset ID efb7b8c949ac4650a09736fc376e9aee [2], enabled by default with Log action to avoid false positives on legitimate Base64 traffic [2]. Attack Score adds a complementary layer, with cf.waf.score.rce able to detect and score secondary payloads such as shell execution primitives or Java class-loading gadgets [2].
By enabling the managed rule, monitoring logs, and layering Attack Score with application-level hardening, teams can reduce the risk of Java4Shell exploitation without changing the application codebase.
References
- A new Cloudflare Web Application Firewall — blog.cloudflare.com (29 March 2021)
- How Cloudflare WAF helps protect against Java4Shell (CVE-2026-114938) — blog.cloudflare.com